Security
Security
How Bhogar protects your data: identity and access controls, tenant isolation, encryption, data handling and retention, deployment options, and compliance status.
Controls
Security controls
Identity and access
- Microsoft Entra OAuth with PKCE; SAML and OIDC for other providers
- Company and workspace scoping on every request, enforced server-side
- Role-based access plus per-module entitlement checks
- MFA with WebAuthn and session revocation
Tenant isolation and data handling
- Tenant identifiers in queries, embeddings, and vector-search filters
- Retrieval filtered by the requesting user’s permissions, not a service account
- Encryption in transit and at rest with managed cloud KMS
- Secrets in a managed vault - never in config or prompts
AI-specific controls
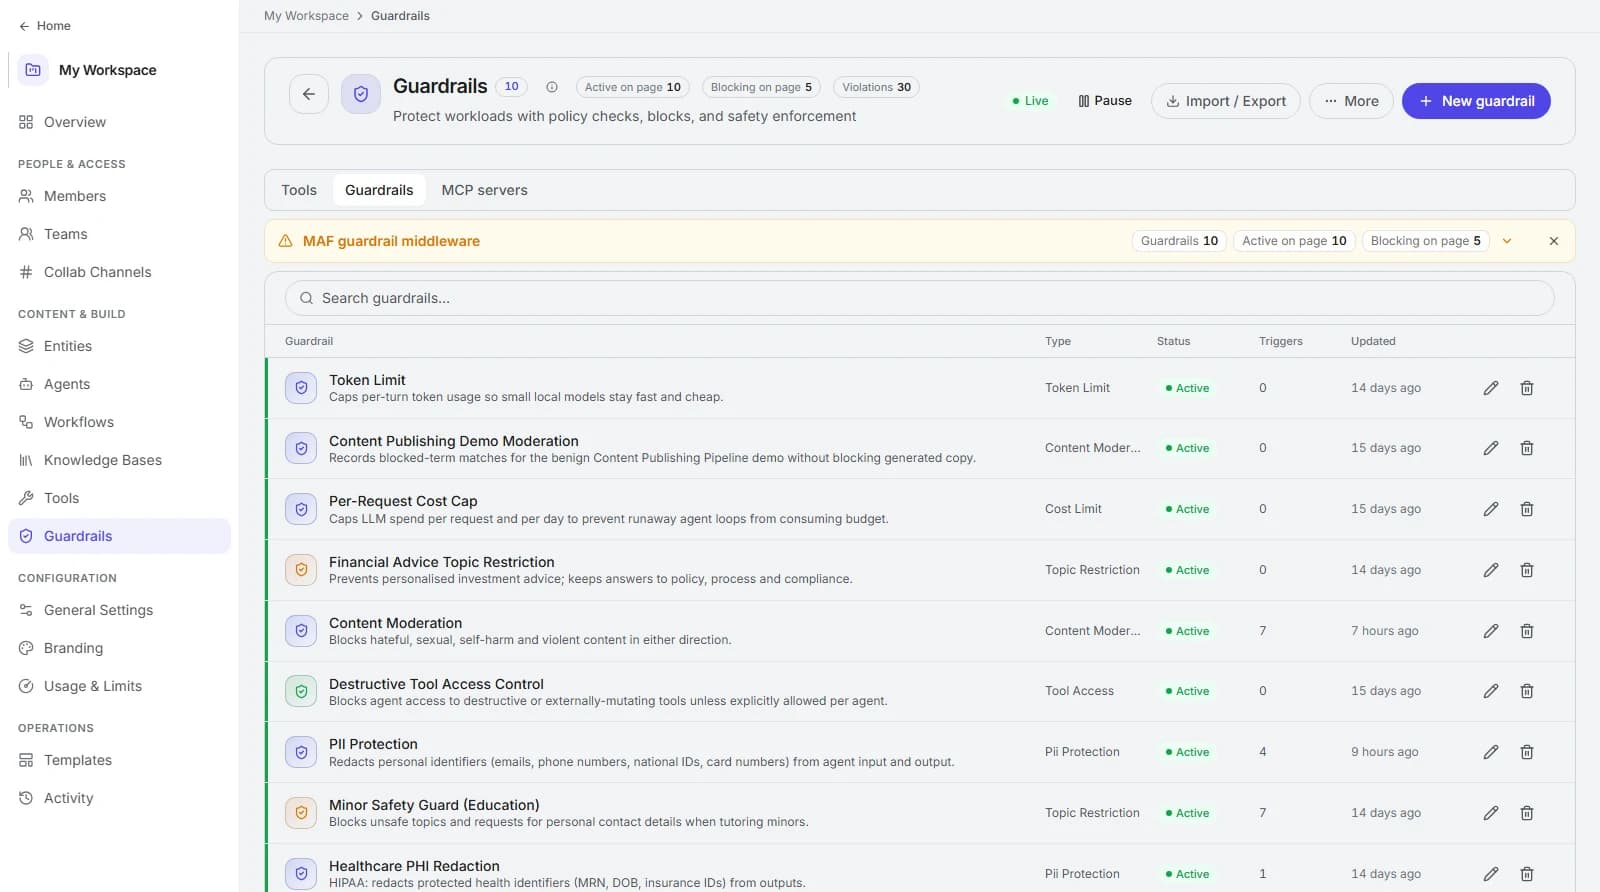
- Guardrails for sensitive-data detection and policy enforcement on input and output
- Model gateway with per-workspace budgets, quotas, and fallbacks
- Evaluation suites that gate changes on quality and safety
- Human approval steps on consequential workflows
Operations and audit
- Execution traces covering retrieval, tool calls, model calls, and cost
- Administrative and access audit history
- OpenTelemetry with pluggable providers, including Azure Monitor
- Container deployment, environment-scoped config, least-privilege identity
Data handling
Data storage and retention
| Category | Purpose | Residency | Retention |
|---|---|---|---|
| Connected source content | Retrieval and grounding | Your tenant database and vector store, in your region | While the source is connected; removed on disconnect or deletion |
| Embeddings and indexes | Semantic search | Same tenant scoping as the source | Rebuilt on re-index; deleted with the knowledge base |
| Conversation and execution history | Continuity, traceability, cost attribution | Platform database in the deployment region | Configurable per company to your policy |
| Model inference payloads | Generating a response or action | The model provider you configure | Governed by provider terms; BYO keys keep it under your control |
| Telemetry and logs | Reliability, performance, security investigation | Your observability backend or the platform default | Time-bounded by your telemetry configuration |
| Credentials and secrets | Authenticating to connected systems and providers | Managed secret store, referenced by ID only | Until you rotate or revoke the connection |
Deployment
Deployment options
Managed cloud
Tenant isolation, regional placement, platform-operated upgrades.
Your cloud subscription
Your Kubernetes; data and model traffic stay inside your network and compliance boundary.
Your model providers
Bring Azure OpenAI, OpenAI, Anthropic, Google, or Bedrock credentials. Inference runs under your agreements.
Compliance
Compliance status
Current status for each framework. Status is confirmed in writing during your security review.
SOC 2 Type II
CertifiedAnnual audits by independent CPA firms for security, availability, and confidentiality controls.
ISO 27001
AlignedInformation security management system aligned with international security best practices.
GDPR
CompliantBuilt for EU General Data Protection Regulation compliance including data subject rights.
CCPA
CompliantCalifornia Consumer Privacy Act compliance with consumer rights protections.
HIPAA Ready
AvailableHealthcare data protection with Business Associate Agreement (BAA) available.
EU-US DPF
CompliantEU-US Data Privacy Framework compliant for cross-border data transfers.
Responsible disclosure
Report a vulnerability
Email security@bhogar.ai with reproduction detail. We acknowledge receipt, work the fix, and coordinate disclosure timing with you. Privacy and data-subject requests go to privacy@bhogar.ai.
Security reviews and questionnaires
Most answers are on this page, in the DPA, and in the SOC 2 alignment document. Send us your questionnaire and we complete the rest in writing.